HUMANX FOR SECURITY LEADERS
AI security is a new category. Get ahead of it before your next board meeting.
HUMANX 2027
MARCH 7-10, 2027
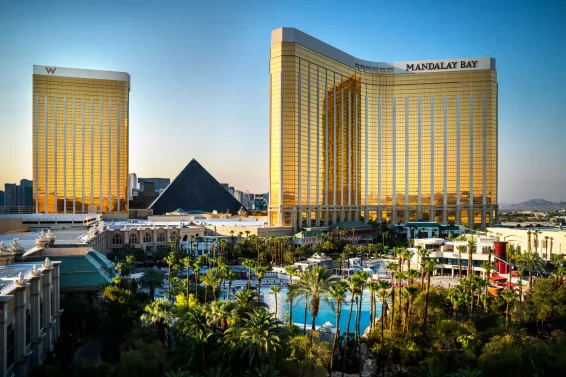
MANDALAY BAY
PHILOSOPHY
Every AI deployment in your organization passes through you.
And the security category around those deployments — model risk, prompt injection, data exfiltration, shadow AI — is less than two years old.
There's no Gartner Magic Quadrant for this yet. There's no mature playbook. What there is: a small group of CISOs who have already navigated an AI-specific incident and are willing to share what they found. HumanX is where that conversation happens.

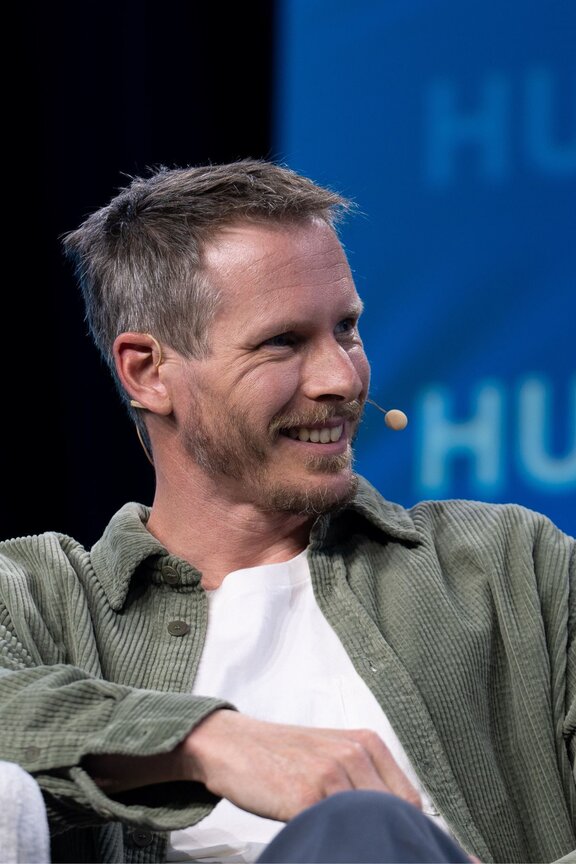
Thomas Wolf, Co-founder & CSO, Hugging Face
WHAT'S ACTUALLY ON STAGE
Technical content built for security practitioners.

Real AI incidents and defenses from CISOs at enterprise organizations — what happened, how they responded, what the post-mortem showed
How leading organizations are implementing the NIST AI Risk Management Framework in practice — the implementation, not the framework itself
How to evaluate a nascent AI security vendor market without a Magic Quadrant to lean on
How to brief organizational leadership on AI risk posture with the credibility to move budget
THE ROOM
The security conversation without the sales conversation mixed in.
A closed-door peer session for CISOs. No vendor reps, no sponsored content, no product pitches dressed up as peer exchange.
What there is: CISOs who have navigated real AI-specific incidents sharing what they found, and a structured environment for the kind of frank exchange that doesn't happen when a vendor is in the room. Beyond the peer session, direct access to leading AI security teams running the models your organization is deploying, and the questions you can't get answered at RSA or at a vendor booth, because the vendors don't run the models.
WHAT YOU'LL LEAVE WITH
A framework stress-tested against real incidents.
LEARN
An AI governance and risk framework stress-tested against real incidents, not just OWASP checklists

CONNECT
A shortlist of AI security tools from a nascent market, with peer validation behind the decisions

DEFEND
Board-ready language on AI risk posture backed by peer benchmarks — not just your own assessment
BUILT FOR YOU
The security conversation without the sales conversation.
A closed-door CISO peer session
Application-required. No vendor reps. Peer CISOs sharing real incidents and real frameworks.
AI security content
Technical sessions on AI-specific risk: prompt injection, model poisoning, data exfiltration, LLM red-teaming.
AI security vendor demos
Discovery-stage buying is about seeing what tools actually do. Live demos, not pitch decks.
Direct access to frontier lab security teams
Structured conversations with high-profile security leadership.

WHO ATTENDS
The leaders rebuilding the stack.
Chief Information Security Officer (CISO)
VP of Security
Head of Security
Head of Cybersecurity
Director of Security Operations
Head of AI Risk
Director of Governance, Risk & Compliance
VP Risk Management
HumanX 2027
March 7–10
Mandalay Bay, Las Vegas